Master Small Business Security (PCI DSS Compliance)

Fraud Protection & PCI DSS compliance is more important than ever. Attackers are increasingly going after businesses, trolling for loopholes and ‘quick wins’ where systems or individual employees haven’t kept up with the technology. Mastercard and other payment card networks see firsthand how fraud is perpetrated and they’ve developed the best practices to guide businesses in beating payment card fraud. It’s important to become PCI DSS compliant and remain in compliance to reduce your likelihood of a costly compromise.

Male small business owner in a workshop using a smartphone to manage payments

Benefits of PCI Compliance

  • Safeguard your business reputation 
  • Increase customer confidence 
  • Reduce risk of account data compromise
icon of checkbox
The PCI Data Security Standard (PCI DSS) is the primary security standard put forth by the PCI Security Standards Council (PCI SSC), a global forum made up of over 800 participating organizations to ensure the security of cardholder data. The PCI DSS and applies to any entity, regardless of size, that stores, processes or transmits cardholder data. 

Technology and expertise provide practical and immediate solutions.

icon of checkbox
When businesses fail to correctly configure the remote access technologies used in their pointof-sale (POS) applications, they provide the most common opening fraudsters are looking for. To reduce your risk of a costly Account Data Compromise (ADC)1 , you should: 
  • Only use approved PIN entry devices and validated payment software at your POS and/or website shopping cart. 
  • Set strong passwords and be sure to change default passwords on hardware and software— most are unsafe! 
  • Use a firewall on your network and PCs. 
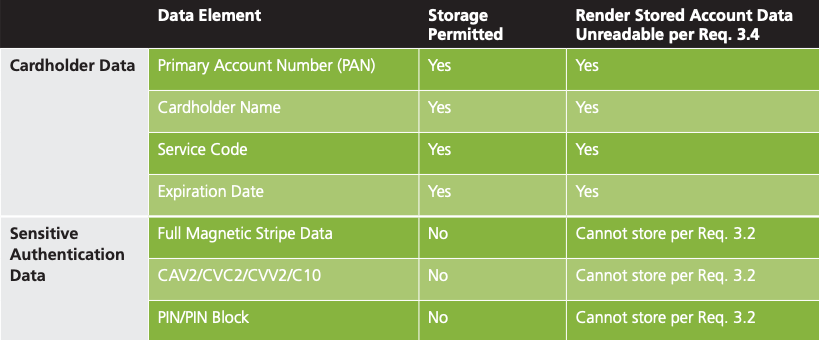
  • Never store ANY sensitive cardholder data after authorization. 
  • Make sure your wireless router is password-protected and uses strong encryption. 
  • Regularly check PIN entry devices and PCs to make sure no one has installed rogue software or “skimming” devices. 
  • Teach your employees about security and protecting cardholder data. 
  • Use two-factor authentication for remote access, in accordance with PCI DSS requirements.
What Cardholder Data Can I Store?
table showing types of cardholder data
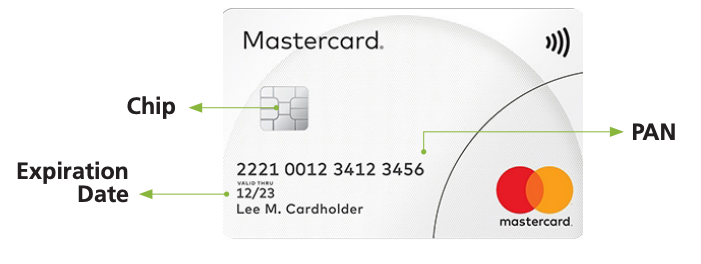
Types of Data on a Payment Card
diagram showing types of data on a payment card
1 - An Account Data Compromise (ADC) event is an occurrence that results—either directly or indirectly—in the unauthorized access to, or disclosure of, cardholder data.

How Can I Find Out More About PCI?

For more information and materials go to:

https://www.pcisecuritystandards.org/
  • Download the Guide to Safe Payments 
  • Attestation of Compliance (AOC) 
  • Self-Assessment Questionnaire (SAQ) 
  • PCI Security Standards 
  • List of Qualified Security Assessors (QSA) 
  • List of Approved Scanning Vendors (ASV) 
  • List of Payment Application Qualified Security Assessors (PA-QSA) 
  • Lists of Approved Payment Applications and Approved POS devices
icon of checkbox

PCI Education Opportunities:

https://www.pcisecuritystandards.org/
icon of checkbox

About Master Your Card

Master Your Card is a community empowerment education program sponsored by Mastercard, that works with committed partners nationwide to bring information about the benefits of electronic payments technology for underserved communities to build brighter financial futures. The program has facilitated presentations and workshops in numerous cities around the country, provided financial education to tens of thousands of students and reached millions through partners’ initiatives and education materials. 

mastercard logo