What are you looking for?
October 6, 2026
Technology has made everyday activities, from communicating to shopping and online banking, infinitely easier. Security advances make our digital lives safer than ever before, too. Yet criminals are always looking for a way in, and there’s one vulnerability that’s very hard to safeguard: human emotion.
In the U.S. alone, consumers lost more than $16 billion to fraud in 2025 — a 25% increase over 2024, according to a Federal Trade Commission report released in June. Nearly one in three fraud reports are related to imposter or impersonation scams, such as fake security alerts from banks or the government — even the FTC itself — asking people to move money to “protect” it.
“Cybercriminals often rely on human emotion like fear, curiosity, sympathy or pride to trick their victims into falling for a con,” says Donna Mattingly, principal of corporate security education and awareness for Mastercard.
Social engineering is a manipulation where criminals trick people to steal money, install malicious software (malware), access business networks for insider info or bring down entire computer networks. Their goals can even include swaying elections or manipulating financial markets. Cybercriminals may email or post fake news stories, press releases or stock performance graphics that trick people into making investments. It can be hard to see what swindlers are after, as their schemes have become incredibly complex.
These attacks work because they exploit fundamental human traits: the desire to be helpful, the tendency to trust authority figures or institutions, and the fear of negative consequences. Scammers create scenarios that trigger emotional responses, making targets act quickly without thinking critically.
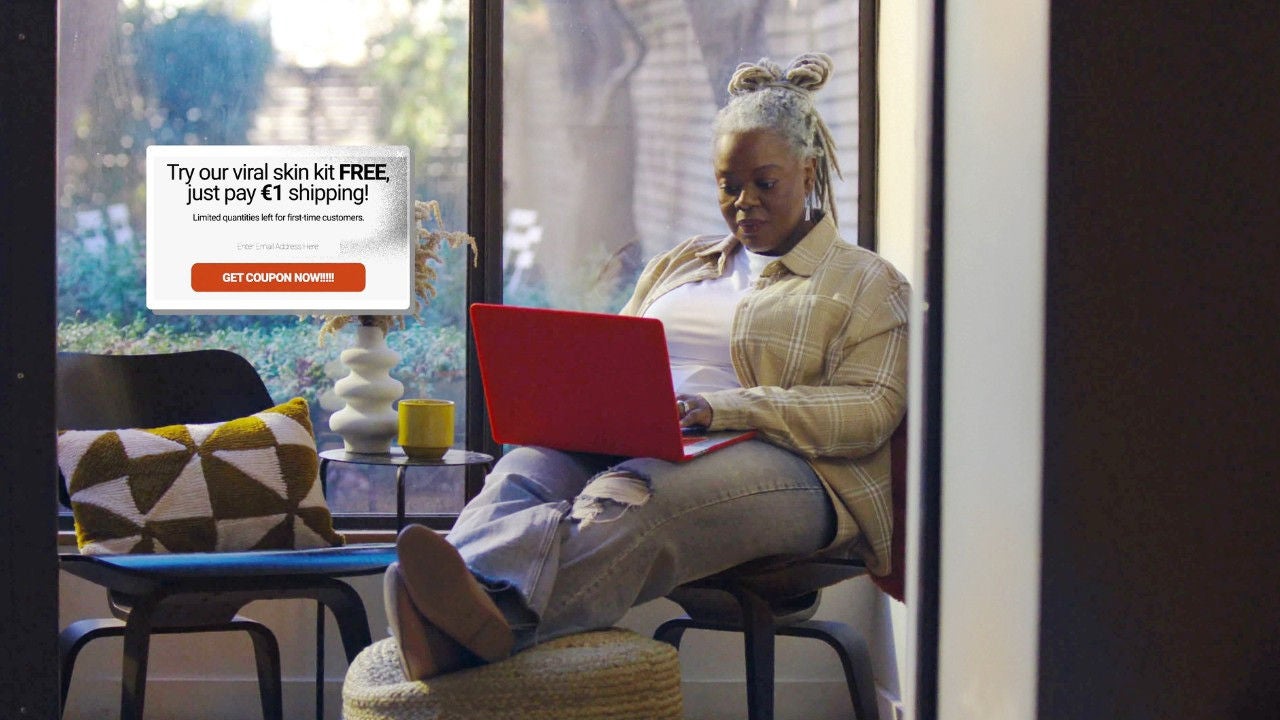
They’ve also become more convincing. Cyber scammers build phony websites and create elaborate false identities to fool their victims. And they’re now using generative AI technologies to create misleading emails, phone calls (gen AI can mimic the voices of your loved ones), images and videos (known as deepfakes) that are so sophisticated, they’re nearly impossible to recognize as bogus.
Even people who’ve been trained to be cautious can be fooled, as evidenced by a 2024 incident in Hong Kong. There, a multinational financial company lost $25.6 million when an employee was tricked into transferring corporate funds to a criminal account. He’d been deceived by a deepfake video conference call with people who looked and sounded like colleagues, including the company’s CFO, but were actually computer-generated impostors.
To protect yourself from cybercrimes, it’s helpful to know what kinds of scams are out there, so you can dodge them.
Social engineering is the use of deception and emotional manipulation to influence someone else’s behavior. In the digital world, cybercriminals use social engineering tactics to trick people into revealing confidential information or taking actions that can harm them, or their employers, financially.
These types of cyber scams can include convincing people to hand over cash or send money electronically. Scammers also use them to obtain personal information like social security numbers, credit card numbers or log-in credentials so that they can later steal money, commit fraud or sell to other criminals.
Social engineering scams may be seeking access to your personal computer or corporate computer network to steal data or intellectual property, install viruses or ransomware (harmful software that locks up files until users pay a ransom) or cause system malfunctions that bring business to a halt.
Their goals can even include swaying elections or manipulating financial markets. Cybercriminals may email or post fake news stories, press releases or stock performance graphics that trick people into making investments.
Social engineering scams take many forms, each designed to exploit different vulnerabilities. Recognizing these patterns helps you identify threats before they cause harm.
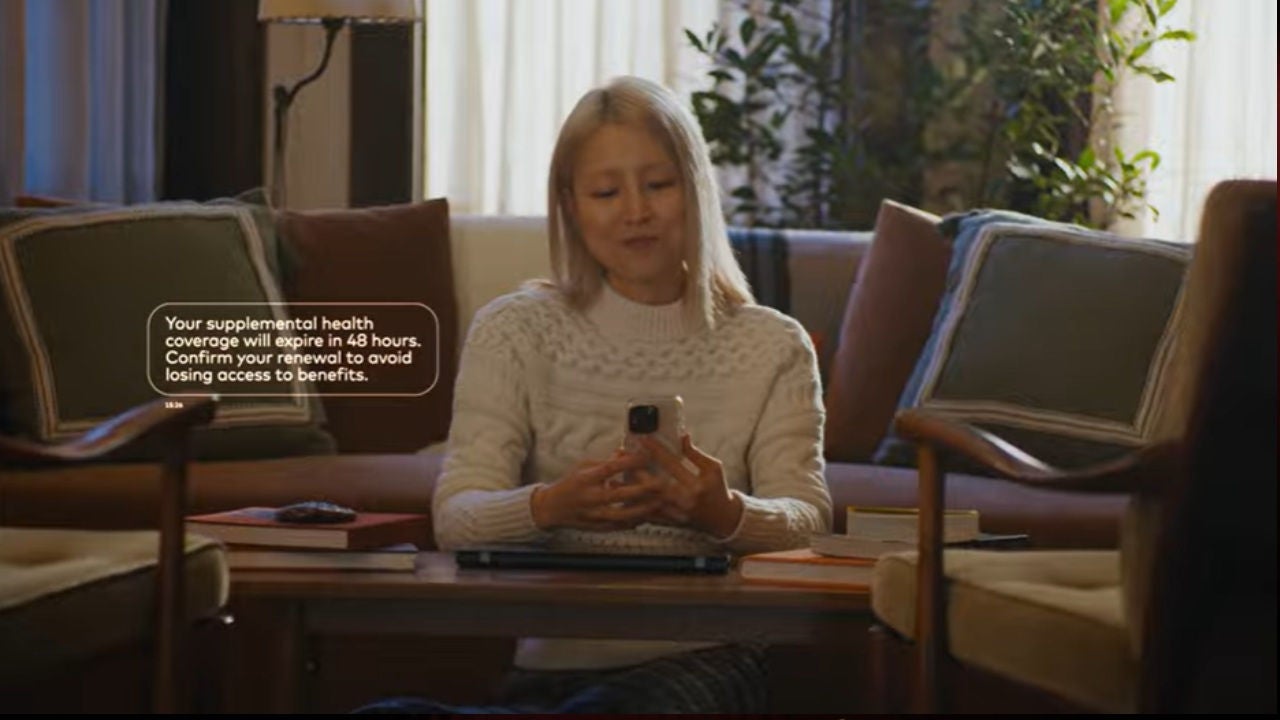
Phishing uses fraudulent emails, websites or messages that appear to come from legitimate organizations to lure recipients into sending money or disclosing confidential information. These messages typically create urgency, claiming your account has been compromised or a payment has failed. They can direct you to fake websites designed to capture your login credentials or payment information.
Remember the “Nigerian prince” emails of the 1990s, where a person claiming to be African royalty requested urgent financial assistance? We may laugh at the premise now, but that widespread scam was one of the earliest and most basic examples of phishing. Since those early days, phishing scams have grown in number and complexity.
Phishing attacks often use messages that inspire fear, panic or other strong reactions. They sound threatening or push for immediate action by presenting urgent situations, such as financial emergencies, the detection of “unusual activity” on your account or unpaid invoices. The aim is to scare people into responding before they have time to think clearly. Many phishing emails ask recipients to click on a link or download an attachment, but doing either can lead to unintended consequences, such as linking to a nefarious website, triggering a computer virus or downloading dangerous software.
Red flags include generic greetings, mismatched sender addresses, and links that don't match the organization's actual domain. Legitimate companies rarely ask you to verify sensitive information through email links.
If you’ve clicked on a phishing link, disconnect your computer or device from the internet. This can interrupt malicious downloads or block them from starting. Scan your system using trusted security software and follow instructions if a virus or malware is detected.
If you typed in a username and password on one of your accounts while visiting a fake website, head to the legitimate site and change them immediately. If there’s any chance you’ve disclosed information that could be used to hurt you financially, contact your bank for instructions on how to proceed.
If you live in a country with credit bureaus, it’s a good idea to contact them. In the U.S., the three major credit bureaus can watch your file for suspicious activity. They will also let you “freeze” and “unfreeze” your credit file for free. Finally, report the cyber scam or fraud to the appropriate authorities and tell friends and colleagues about the scam so they won’t be baited into repeating your mistake.
Vishing attacks happen over the phone. Scammers impersonate bank representatives, government officials or tech support agents. They may spoof caller ID to display legitimate phone numbers, making the call appear authentic.
Common vishing scenarios include calls about suspicious account activity, tax problems requiring immediate payment, or computer viruses that need urgent attention. The caller creates pressure to act immediately, often requesting payment through gift cards, wire transfers or cryptocurrency.
Smishing delivers phishing attacks through text messages. These messages often claim to be from delivery services, banks or government agencies. They include links to malicious websites or phone numbers that connect to scam call centers.
One recent pervasive smishing scam tells recipients that they have an unpaid balance on a toll road, and they must pay the balance or risk legal action. Package delivery scams have become particularly common, with messages claiming a delivery failed and requesting a small fee or address confirmation through a fraudulent link.
Spear phishing is a targeted, more personalized form of phishing. Scammers do their research before initiating contact, so they can address you by name or claim to represent a company or a person you know.
Often they’re able to glean a lot of detail form social media, so consider using privacy settings on social media sites to limit the exposure of your posts.
Whaling is a targeted phishing attack that’s aimed directly at corporate executives or other high-ranking individuals. In other words, the big fish (“whales”) in an organization.
Quishing is a type of phishing where scammers convince people to scan a fake QR code that takes them to a malicious website, where they may be persuaded to give up confidential information or download harmful software.
Zishing is a phishing technique that takes place on videoconferencing calls and uses deepfake technology to fool victims. The “z” stands for Zoom, but it can happen on any platform.
Angler phishing targets social media users who’ve posted complaints about a business or service. Fraudsters create fake social media profiles and then contact the original poster, posing as a customer service representative who wants to help. They’ll ask for personal information and use it for criminal activity.
Email spoofing is when scammers hide their identity by disguising their email address or display name, so emails appear to come from someone the recipient recognizes. Sometimes scammers use email accounts so close — maybe differing by only one letter — that recipients fail to spot the discrepancies.
Business email compromise targets organizations by impersonating executives, vendors or partners, with emails crafted to convince other employees to reveal privileged financial information or authorize payment transfers that send money to fraudulent accounts. These attacks often coincide with real business events like mergers, vendor changes, or executive travel. The timing makes fraudulent requests appear legitimate.
A scareware attack frightens computer users into installing malicious software or opening virus-infected files. A user may receive a pop-up notification falsely warning that their computer has been infected with a dangerous virus. They’re then instructed to purchase fake software or send money to unlock the computer.
Romance scams are when criminals create realistic profiles on dating apps and websites or social media platforms and feign romantic interest in potential victims. Dangling the promise of a relationship, they ask for money, push fraudulent investment or cryptocurrency schemes or request personal details to access financial accounts.
These often unfold over weeks or months, and they often work around dating site safeguards by proposing a move to texts or emails soon after conversations begin.
Investment scams promise high returns with little risk. Common types include Ponzi schemes that pay early investors with money from new victims, pump-and-dump schemes that artificially inflate asset prices, and fake cryptocurrency or trading platforms.
Social engineering tactics in investment scams include creating false urgency, using fake testimonials, and building affinity through shared interests or community connections. Scammers may pose as successful investors or financial advisors, sometimes using stolen credentials or fabricated licenses.
One recent operation named after the film “The Truman Show,” about a man who unknowingly lives within a reality TV show, lured potential victims into WhatsApp and Telegram groups entirely populated by AI-generated experts and other institutional traders. It created the appearance of a legitimate community, simulating a trustworthy environment where the victim could be convinced to share identity documents or fund accounts.
Red flags include guaranteed returns, pressure to invest quickly, requests to keep the investment secret, and difficulty withdrawing funds.
Prevention is more effective than recovery. These practices reduce your vulnerability to social engineering attacks.
Never use contact information provided in a suspicious message. Look up phone numbers and websites independently. When someone claims to represent your bank or card issuer, hang up and call the number on the back of your card.
For unexpected requests from family or friends, especially those involving money, verify through a different communication channel or ask questions only the real person would know.
Discuss common scam tactics with elderly relatives and teenagers, who are frequently targeted. Establish family protocols for verifying emergency requests, including code words that confirm identity.
Consider setting up account alerts that notify multiple family members of large transactions. Review the A-Z cybersecurity guide together to build shared awareness.
Organizations face targeted attacks including business email compromise and invoice fraud. Implement these controls:
Stop all communication with the suspected scammer and contact your card issuer immediately to report the fraud and request a block on further transactions. Change usernames and passwords and enable multifactor authentication for digital interactions. Document everything including transaction records, messages, emails, and phone numbers used by the scammer
Help future victims by reporting the crime. Most countries have a central authority that handles cyber scams and fraud. In the U.S., contact the Federal Trade Commission through its website or by calling 877-IDTHEFT (438-4338). Europol has a list of member states with individual reporting websites.
This story was originally published March 7, 2024 and has been updated with new statistics from the FTC and new examples of scams.
Please accept functional cookies to watch this video.